See where you stand on AI readiness and cyber risk.
Use a focused, directional assessment to identify foundational gaps across governance, cybersecurity and AI readiness, then decide what deserves deeper review.
Free · about 5 minutes · no sign-up required to complete the questions
Foundational controls create the conditions for safer AI adoption.
The assessment combines core cybersecurity capabilities with AI-specific governance questions. It is designed to surface issues that often affect AI initiatives: ownership, data protection, identity, vendor risk, monitoring, incident response, AI inventories, risk assessment and ongoing management.
NIST CSF 2.0
Govern, Identify, Protect, Detect, Respond and Recover provide a structured view of core cybersecurity capabilities.
NIST AI RMF
Govern, Map, Measure and Manage help organize AI-specific accountability, context, assessment and treatment.
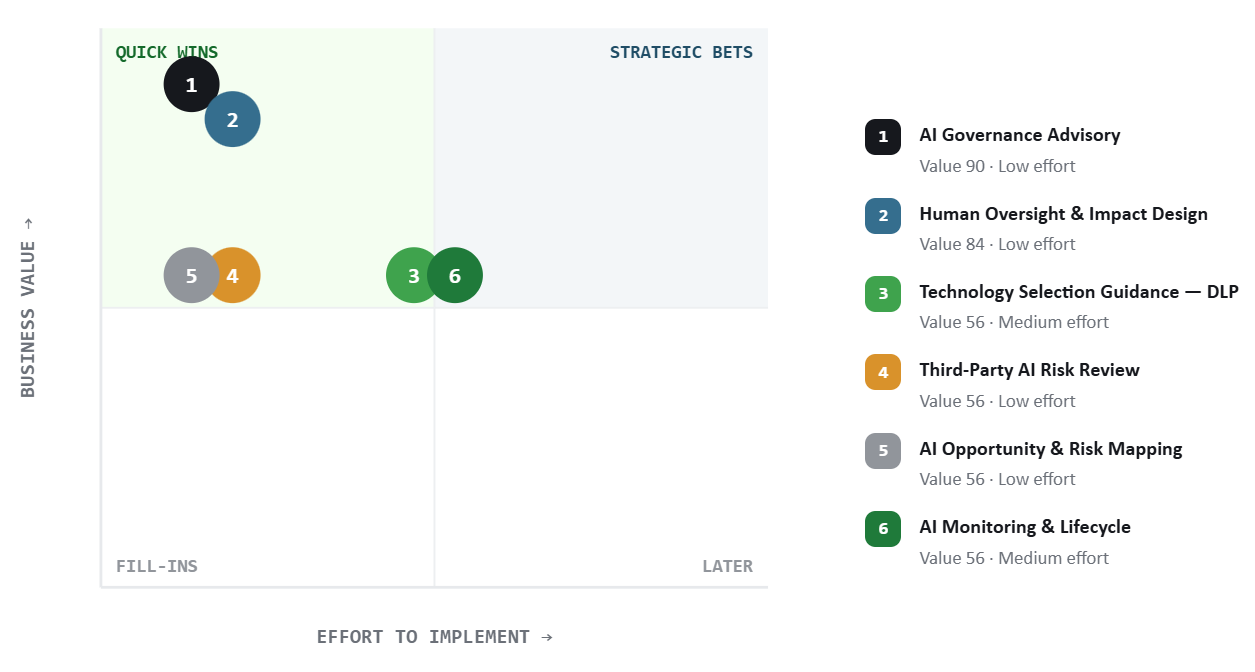
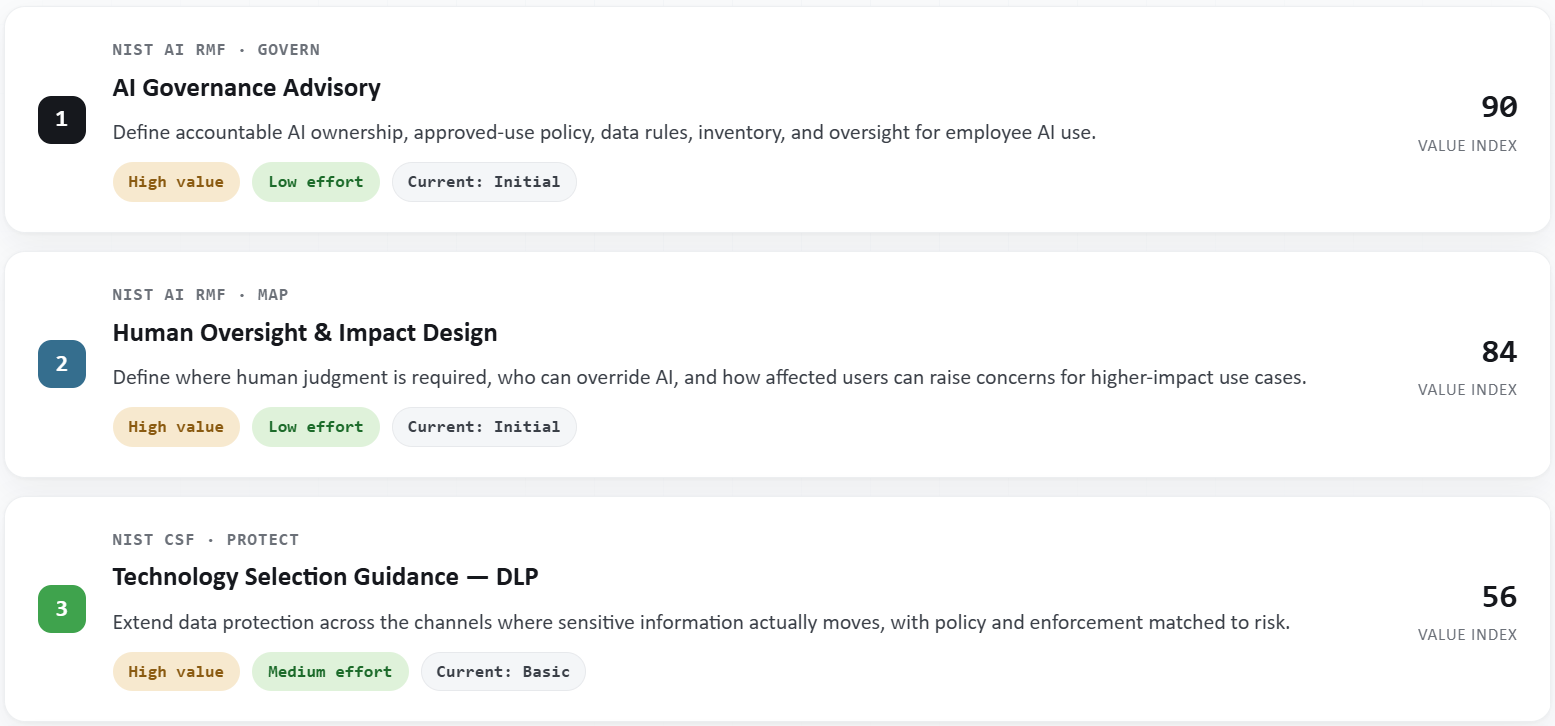
Prioritized next steps
Scores are used to identify areas for deeper review and discussion rather than replace a formal audit or certification assessment.
A report you can use to frame the next conversation.
- Directional cybersecurity maturity and AI readiness views
- Functional breakdown across NIST categories
- Priority gaps based on your responses
- Recommended areas to address first
- A phased roadmap view
- Optional email copy and advisor follow-up after full completion
Complete the assessment without creating an account.
Answers remain in the browser during the session. If you complete the assessment and choose to email the report, your contact details and report are submitted for delivery and advisor follow-up.
Use the results to identify where deeper work may be needed.
Formal compliance, certification and audit work requires a defined scope, evidence and—where applicable—qualified or accredited assessors. Cybersafer can help determine the appropriate next step.
See where you stand.
Complete the assessment and review your report immediately. If you want help interpreting the results, you can choose to email the report and request advisor follow-up.
Start the assessment →